By: Jay Kt
Pharmaceutical and life sciences organisations now depend on connected systems at almost every stage of their work. Research data is stored in the cloud, manufacturing lines are controlled by networked equipment, and medical devices exchange data with hospital and laboratory networks. That connectivity brings practical benefits, but it also widens the attack surface. A compromised account, an unpatched device, or a poorly controlled supplier connection can disrupt production, expose sensitive data, or create a regulatory problem that takes months to close.
Regulators have responded by tightening expectations. In June 2025, the US Food and Drug Administration issued updated final guidance on cybersecurity in medical devices, covering design, labelling, and documentation for premarket submissions, including software bills of materials and plans for monitoring vulnerabilities. The guidance reflects a broader shift: cybersecurity is now treated as part of product and system design, not as a task added after deployment.
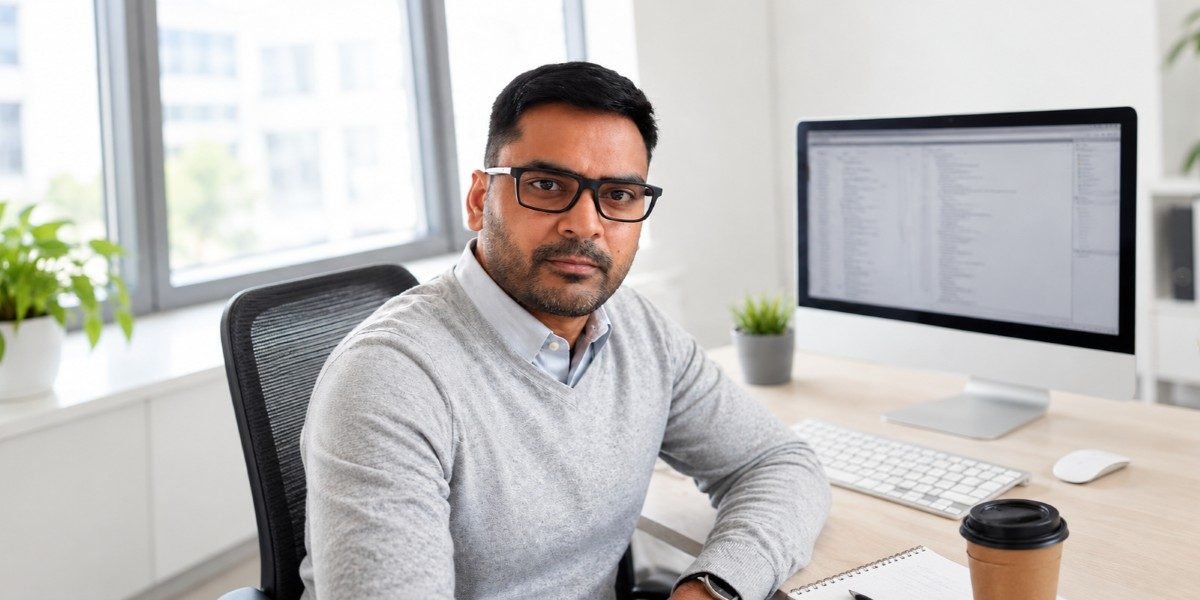
Prasanth Alluri‘s career sits within that shift. He is an Infrastructure and Security Architect at Celito Tech, a managed service provider for pharmaceutical and life sciences organisations. His earlier work was in physical infrastructure and software development, before he moved into cloud engineering, security operations, and enterprise security architecture.
From Physical Infrastructure to Software
Alluri holds a Master of Science in Mechanical Engineering and a Master of Science in Information Technology. Early in his career, he worked as Managing Partner at A.M. Raju and Co., directing bridge construction projects from feasibility and design through procurement, construction, commissioning, and handover. Bridge projects cross wetlands, rivers, and ecologically sensitive zones, so environmental impact assessments and mitigation planning were part of the job. Quality assurance covered materials certification, inspection protocols, and construction tolerances, while strategic planning covered bids and expansion across public and private sectors. A mistake in that world was not abstract. It was visible, costly, and sometimes irreversible.
He later moved into software development at Tera Software Limited, building ASP.NET Web Forms applications and WCF web services, working on state management, caching, and secure application design. The shift from concrete and steel to code was not a break from his earlier work. It was the same engineering instinct in a new medium: build carefully, understand the load the system must carry, and leave nothing important to chance.
That experience still shapes his approach to cybersecurity. He treats digital infrastructure with the same seriousness: define the requirements clearly, test the tolerances, document the controls, and plan for change. Security, in his work, is not added at the end of a project. It is part of the structure itself.
Public APIs at the World Bank
From 2014 to 2016, Alluri worked as a DevSecOps Engineer at the World Bank. There, he worked on public-facing Open Data API infrastructure, including authentication, encryption, and rate limiting, so that public data could be shared widely without the service being misused or overwhelmed.
He also worked on an AWS cloud migration, provisioning highly available EC2 infrastructure with Terraform and CloudFormation and embedding security controls directly into it. He developed an automated security testing framework for API endpoints, designed disaster recovery protocols, and built Tableau dashboards to make threat and compliance information easier to act on.
The lesson was practical and enduring: security must work at speed. A system that slows legitimate use to a crawl will be bypassed, while a system that moves fast without controls will eventually be exploited.
Security Work Inside a Pharmaceutical Enterprise
From 2016 to 2023, Alluri served as Senior Information Security Engineer at AbbVie, where the stakes were shaped by regulation, patient safety, and the complexity of a global life sciences company.
He worked on endpoint detection and response deployment, built Splunk dashboards and correlation searches for monitoring, threat hunting, and compliance tracking, and turned large volumes of security data into decisions teams could act on quickly.
He also worked on enterprise security consolidation following acquisitions, integrating identity and access management systems and simplifying environments that had grown complicated through mergers. Every duplicate system, unclear permission, and forgotten account is a potential opening, and simplifying the environment made it easier to defend.
His access review and least-privilege work focused on removing permissions that were no longer needed. He managed a McAfee ePO environment for malware protection and compliance across hybrid infrastructure, conducted security architecture reviews, and presented security metrics to executives, connecting technical findings to business risk and leadership decisions.
Zero Trust, Explained
Zero trust is one of the central ideas in Alluri’s current work, and it is worth explaining in plain terms because the phrase is often used loosely.
In a traditional network model, a user or device inside the office network was often treated as trusted. Zero trust removes that assumption. The US National Institute of Standards and Technology, in Special Publication 800-207 on zero trust architecture, describes a model in which no entity is trusted by virtue of its location alone, and access is verified before it is granted. In practice, that means checking identity, checking device health and context, granting only the minimum access needed for the task, and repeating those checks rather than treating a single login as permanent permission. It also means segmenting systems so that one compromised account cannot easily reach everything else.
Since January 2024, Alluri has worked as Infrastructure and Security Architect at Celito Tech, serving pharmaceutical and life sciences organisations. His focus is zero-trust security across multi-cloud environments spanning AWS, Azure, and Google Cloud, together with enterprise identity, privileged access, and multi-factor authentication work.
He has also established security programmes aligned with the NIST Cybersecurity Framework, NIST 800-53, and ISO 27001, conducting gap assessments and building remediation roadmaps. In life sciences, audits and third-party assessments are part of continuous operation, so his policies, standards, and technical controls are built to support them year-round.
He has also engineered high-availability and disaster recovery architectures for mission-critical operations. For pharmaceutical operations, downtime can disrupt research, manufacturing, and patient-facing work, so a secure system that is not available is still a failed system.
His certifications include GIAC Public Cloud Security, GIAC Information Security Professional, GIAC Certified Incident Handler, CompTIA Security+, Splunk Core Certified Power User, and CyberArk Trustee. His compliance work spans NIST, ISO 27001, HIPAA, FDA 21 CFR Part 11, and GxP requirements.
Why Cybersecurity Matters in Life Sciences
Pharmaceutical and life sciences organisations face a specific combination of risks. Research data and manufacturing know-how are valuable targets. Production systems must keep running, because an interruption can affect supply. Connected medical devices must be protected without disrupting clinical work. And every control must be documented, because regulators, auditors, and customers will ask for evidence.
That is why the FDA’s updated 2025 guidance matters beyond device manufacturers. It signals that security documentation, vulnerability monitoring, and update planning are expected parts of a product’s lifecycle. The same expectation reaches service providers and enterprise security teams: they must be able to show what was protected, how access was controlled, and what happens when a vulnerability is found.
Alluri’s published research addresses parts of the same problem from an academic angle, as described below. The research proposes and analyses frameworks and approaches, which is a different kind of contribution from operational deployment, and that distinction matters for how the papers should be read.
Research on Security, Health, and Infrastructure
Alluri’s Google Scholar profile lists eight publications. The five most relevant to cybersecurity are described here, with their journal and year. Where a paper proposes a framework or analyses an architecture, it is described that way, not as a deployed technology.
His 2024 paper, “Zero-Trust and Artificial Intelligence-Driven Security Strategies for Cyber-Physical Systems in Pharmaceutical and Defense Facilities,” published in Membrane Technology, pages 794 to 825, examines zero-trust and AI-driven security strategies for cyber-physical systems in pharmaceutical and Defence settings.
His 2023 paper, “Cyber Risk Modeling and Security Governance for Networked Medical Devices in Critical Healthcare Infrastructure,” published in the Journal of Computational Analysis and Applications, volume 31, issue 4, pages 2675 to 2714, presents a risk modelling and governance approach for networked medical devices.
His 2024 paper, “An AI-Enabled Cybersecurity Framework for Securing Medical and Pharmaceutical Manufacturing Ecosystems,” published in the Journal of Information Systems Engineering and Management, volume 9, issue 4s, pages 3774 to 3796, develops and conceptually validates a layered AI-enabled framework for manufacturing security. The paper describes the framework as proposed and conceptually validated, based on a review of literature, standards, and regulatory guidance, rather than as a system proven in production.
His 2023 paper, “Privacy-Preserving Intrusion Detection in Pharmaceutical Information Systems Using Federated Learning,” published in the Journal of Computational Analysis and Applications, volume 31, issue 4, pages 2559 to 2593, addresses intrusion detection in pharmaceutical information systems using federated learning, an approach in which models are trained without centralising all raw data in one place.
His 2022 paper, “Behavior-Based Cyber Defense Architectures for Enhancing the Resilience of Defense and National Critical Infrastructure,” published in the Journal of Electrical Systems, volume 18, issue 4, pages 214 to 236, proposes and analyses a behaviour-based reference architecture for defence and critical infrastructure.
His Scholar profile also lists three infrastructure papers outside the cybersecurity focus: “Data-Driven and Artificial Intelligence-Enabled Frameworks for Sustainable Energy, Rural Transportation Networks, and Water Resource Management in Developing Economies,” published in the International Journal of Communication Networks and Information Security, volume 14, issue 3, in 2022, pages 1498 to 1521; “AI-Driven Optimization of Energy-Efficient Rural Road Infrastructure and Water Conservation Systems in Resource-Constrained Regions,” published in the International Journal of Intelligent Systems and Applications in Engineering, volume 12, issue 23s, in 2024, pages 4088 to 4102, which uses a model-based analytical approach and scenario-based simulations; and “Integrating Artificial Intelligence for Climate-Resilient Energy Planning, Rural Infrastructure Development, and Water Conservation in Underdeveloped Regions,” listed in Computer Fraud and Security in 2024. Those papers reflect the same infrastructure background as his early bridge work, applied through data-driven and AI-assisted planning methods.
His research record is also documented through his ORCID profile, which identifies him as Infrastructure and Security Architect at Celito Tech.
Working Across Teams, Audits, and Compliance
The work described above is, in practice, work across teams. Consolidating identity systems after an acquisition, redesigning access controls across multiple clouds, and preparing for audits all require coordination with engineering, operations, compliance, and executive teams. Alluri’s work includes risk assessments, gap assessments, remediation roadmaps, security architecture reviews, and executive reporting.
That coordination is where frameworks stop being paperwork. A gap assessment only matters if it leads to a prioritised fix, a control only matters if it is verified, and a metric only matters if it makes risk visible enough to be managed. In regulated environments, documentation is itself part of the work, because an undocumented control is difficult for an auditor or a customer to rely on.
From Physical Infrastructure to Digital Resilience
Prasanth Alluri’s career moves from physical infrastructure, through software development, to cloud and security architecture in regulated organisations. The throughline is not a single technology. It is the task of designing systems that can be checked, audited, and kept running under pressure, whether the system is a bridge, a public API, an enterprise endpoint estate, or a multi-cloud environment serving pharmaceutical clients.
That task is becoming more central, not less. As pharmaceutical and life sciences systems become more connected, and as regulators ask for stronger evidence of control, the work of defining access, monitoring behaviour, and documenting security decisions will continue to sit alongside research and manufacturing themselves. For Alluri, the journey from bridge construction to cybersecurity is not about leaving one field behind. It is about carrying the same responsibility forward: build it right, prove that it can hold, protect the people who depend on it, and keep improving the structure as the world around it changes.